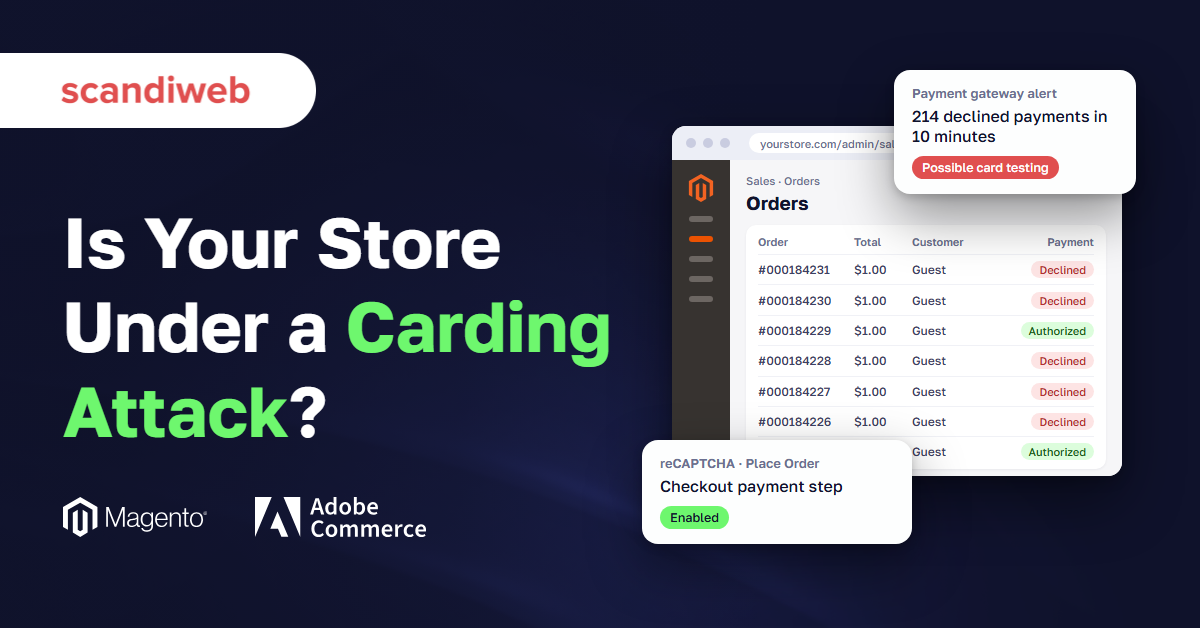
A carding attack is fraud in which bots run stolen card numbers through an online store’s checkout, using small or zero-amount payments, to find out which cards still work. The store whose checkout gets used pays for the tests.
The carding attack we handled began with a sudden spike in orders on a store we look after. Every order had the same shipping address, and the customer details were obviously fake. Many were paid with cards that went through, and the automated fraud screening flagged none of them. It could have passed for a very good sales day.
A store owner looking at orders like these has two questions. Is this what is happening on my store? And what do I do in the next hour?
What is a carding attack?
A carding attack is payment fraud in which criminals use bots to run stolen card numbers through an online store’s checkout, to learn which cards still work before they sell or spend them. People also call it card testing, and Stripe’s card testing guide lists enumeration as another name. Visa says enumeration causes about $1.1 billion in fraud losses a year.
The card numbers are stolen elsewhere first, in data breaches, through phishing, or with skimming code on a checkout, as in the card-skimming case we investigated.
Scripts then send many cards through a checkout and read each authorization, the bank’s yes or no for a card before money moves. Stripe says the tests are card setups without a charge, or small payments the cardholder is unlikely to notice.
The cards that pass are used for bigger purchases or resold, often a year or more later, Visa’s Fall 2025 threats report found.
Carding fraud works best where the payment step answers at once, guest checkout needs no account, and a cheap product keeps each test small. A Magento (Adobe Commerce) store gets picked for the same reasons, and Adobe’s docs say its merchants can be targeted through their storefronts and payment gateway integrations.
Carding, card testing and enumeration: what is the difference?
Carding attack and card testing attack are two names for the same thing: checking stolen cards at a store’s payment step. Enumeration is Visa’s word for testing or guessing card details, such as the expiry date or the CVV, the card’s security code. Card skimming is the earlier theft, when code hidden on a checkout copies the card details.
| Term | What the attacker has | What they do at your checkout | What you see |
|---|---|---|---|
| Carding (card testing) | Real stolen card details | Run each card through a small payment | Bursts of small orders that share details, many approved |
| Enumeration | Part of a card, such as the number without the CVV | Guess the missing details with scripts | Mostly declines, often in one BIN range (the first digits of a card number, which identify the bank) |
| Card skimming | A way to add code to a checkout | Hide a script that copies what shoppers type | A form or script on the checkout that your team did not add |
🚀 Quick takeaway
Ask your payment provider for today’s declines grouped by BIN. Adyen says enumeration scripts guess inside specific BIN ranges, so one range failing repeatedly is the tell.
How do you know your store is under a carding attack?
Your store is under a carding attack when many payment attempts arrive close together and share things real shoppers would not share, such as one shipping address. Adobe’s Traffic Insights playbook calls this “high-volume, low-diversity” traffic. It shows in five places.
- In the orders grid, orders for one low-priced product arrive in rapid succession, with repeating names or addresses
- In the payment provider’s dashboard, volume and declines jump together, and the same decline reasons repeat
- On the provider’s invoice, authorization fees rise with no revenue to match
- On the server, load climbs from near-identical checkout requests
- Weeks later, in your provider’s dispute queue, disputes and early fraud warnings arrive from cardholders who never ordered from you
Stripe’s engineers reported in January 2025 that attackers now test real stolen card data, so a low approval rate is no longer a reliable signal. In the attack we handled, valid cards went through and fraud screening flagged nothing.
A real sales spike from a promotion or Black Friday looks different. Real buyers choose varied products and amounts, many have order history, and the decline rate stays near a normal day’s.
🚀 Quick takeaway
Sort today’s orders by shipping address. In the attack we handled, one address repeated across the whole spike.
What does a carding attack cost a merchant?
A carding attack costs the merchant in stages: fees on every attempt, stock lost to fake orders, then refunds and chargebacks on the cards that passed. A chargeback is a payment the cardholder’s bank takes back after a dispute. Enough of them can put the store in a card network monitoring program.
Stripe lists authorization and dispute fees among the consequences of card testing. Visa also charges $0.10 for each excess retry of the same card on domestic payments, according to PayPal’s May 2026 summary.
The test orders hold stock a real customer could have bought, and Visa warns that merchants can lose inventory fulfilling orders for non-customers. Later, cardholders dispute the charges on the cards that passed.
Disputes count toward Visa’s Acquirer Monitoring Program (VAMP). Its fact sheet sets the Excessive Merchant threshold for fraud reports and disputes at 150 basis points (1.5%) of settled transactions in the US and EU from April 1, 2026. VAMP also requires acquirers, the banks behind payment providers, to act on merchants that pass its enumeration thresholds.
A carding attack we stopped: what happened
We stopped the attack by disabling the product the bots were ordering and blocking their IP addresses, which bought us time. The lasting fix was CAPTCHA on the checkout, a test that tells people from scripts, and rate limiting, a cap on requests per visitor.
The orders looked real and arrived in rapid succession, all for the same low-priced product and the same shipping address, with fake customer details and repeating IP addresses. Many used valid card details, and the automated fraud detection flagged neither the orders nor the payments.
A distributed attack spreads the orders across many customers and IP addresses, and the pattern shows only on closer inspection.

The requests put a heavy load on the servers and could have used up the product’s stock. The larger damage comes later, as chargebacks. The delivery addresses are fake, so nobody is waiting for the parcels.
After identifying the pattern, we worked in this order.
- We disabled the products being ordered, and the orders stopped. The attacker kept sending requests and could have switched products.
- We blocked the attacking IP addresses. This was a stopgap, since real customers share public IPs and the attacker could move to a VPN.
- We watched new orders closely while we worked on a permanent fix.
- We put CAPTCHA on the checkout and rate limiting at the infrastructure level.
Today we would also turn on the payment rate limiting built into Magento 2.4.7 and later, and ask the payment provider to switch on its own card testing rules.
🚀 Quick takeaway
After you disable a targeted product, check the server logs for checkout requests that keep coming, as they did in our case.
How to stop a carding attack in the first hour
To stop a carding attack in the first hour, confirm it, call your payment provider, and put CAPTCHA and rate limits in front of the checkout before you block anyone by hand. Then remove the product the bots are using and clean up the test orders.
- Confirm it. Compare declines per hour with a normal day, and note what the attempts share, such as the product or the email pattern.
- Call your payment provider. Say when it started and ask which card testing protection they can switch on, such as Stripe’s Radar rules, Braintree’s risk threshold rules, or Adyen’s “bot attack risk” rule. Ask them to block the BINs and patterns they see.
- Make the checkout harder to script. Put CAPTCHA on the order step and the coupon form, and rate limits at the firewall or CDN, the layers that filter and deliver your traffic. On Magento, checkout reCAPTCHA is built in and off by default, and our Magento fraud prevention guide has the settings.
- Take away the target. Disable the product the bots are ordering, or set a minimum order value for the night.
- Block with care. An IP block is a stopgap, and Stripe warns that IP-only firewall rules are “usually not sufficient,” so combine IP with other signals, such as an email pattern.
- Clean up the orders. Cancel the test orders and never ship them. Void, or cancel, authorizations that have not been captured, which Stripe says keeps them out of fraud reports. Refund captured charges before they become chargebacks.
- Keep a record of the start time, order numbers, IP addresses, and decline codes for your provider.
Our Magento support team can take these steps for you.
Carding attack prevention: what to keep in place
Keep the controls from the attack switched on, so the next wave of bots fails early. We advise CAPTCHA on the checkout, rate limiting on payment requests, a firewall with bot protection, your payment provider’s rules, and an alert on failed payments.
- Keep CAPTCHA on the checkout. Visa says to validate it on every request that checks a card, and on Magento, calls made with integration tokens skip reCAPTCHA
- Turn on rate limiting for payment requests. Magento 2.4.7 and later, in Adobe Commerce and Magento Open Source, has it at Stores > Configuration > Sales > Sales > Rate Limiting. It is off by default, and Adobe’s rate limiting docs say it silently does nothing until the Redis logger is configured
- Put a firewall and bot protection in front of the store. On Adobe Commerce on cloud infrastructure, Adobe lists rate limiting and bot mitigation as outside what the included Fastly firewall provides, and the paid Advanced Security add-on adds them. Self-hosted stores get this layer from their Magento hosting provider or CDN
- Leave your payment provider’s card testing rules on, and require CVV and address checks, as Visa recommends
- Set an alert on failed payments per hour, sent to someone who can act
- Before peak season, confirm that every control here is still switched on
Our Magento 2 security guide covers the rest of store security.
🚀 Quick takeaway
On Magento 2.4.7 or later, search your logs for Backpressure sliding window not applied. That line means rate limiting is enabled with no Redis logger behind it.
Frequently asked questions
Why do carders pick a particular online store?
Carders pick a store that checks cards quickly and asks few questions. Visa names eCommerce merchants with weak fraud controls as the most common way in, and Stripe notes that guest checkout is easier to abuse than a login. A payment step that answers at once helps too.
Who pays for a carding attack?
The merchant pays. Stripe counts authorization and dispute fees among the costs of card testing, and the card networks charge retry fees when one card is tried too many times. The merchant also refunds the cards that passed or answers the disputes on them.
Does a CAPTCHA stop carding attacks?
A CAPTCHA stops scripts when it guards every request that checks a card or takes a payment, as Stripe and Visa both advise. Alone, it leaves gaps. On Magento, Adobe’s list of protected GraphQL mutations leaves out placeOrder, so pair it with rate limiting.
Can a carding attack put my store in a card network monitoring program?
Yes. Stripe’s guide to Visa’s VAMP says a merchant is Excessive for enumeration when flagged authorizations pass both 300,000 and 20% of all authorizations, and that Visa assesses no fines for it. Fees apply in the separate fraud and dispute category.
How do I report a carding attack?
Report it to your payment provider first, with the start time, order numbers, and IP addresses. Visa’s merchant guide also asks merchants to send attack details, including IP addresses, billing address, email, and User-Agent, to [email protected]. Your provider or bank can say who else to tell.
Main takeaway
A carding attack uses your checkout to test stolen cards, and you pay for every test, first in fees and later in refunds and chargebacks. Approved payments are no proof of real customers, because the cards being tested are often real, so look at what the orders share.
In the first hour, confirm the pattern, call your payment provider, and put CAPTCHA and rate limits in front of the checkout. Remove the product the bots are using, void or refund the test orders, and treat IP blocks as a stopgap.
Afterward, keep those controls switched on and check them before every peak season.
If bots are hitting your checkout right now, send us the time it started and the name of your payment provider, and we'll help you stop it.


Share on: